Close the loop
on information risk
RiskLoop360 takes you from a blank scope to an audit-ready risk management system: identify assets and threats, score and prioritise risk, map mitigations to ISO 27001, NIST, and more, generate policies — then loop back through audits and reviews to keep it all current.
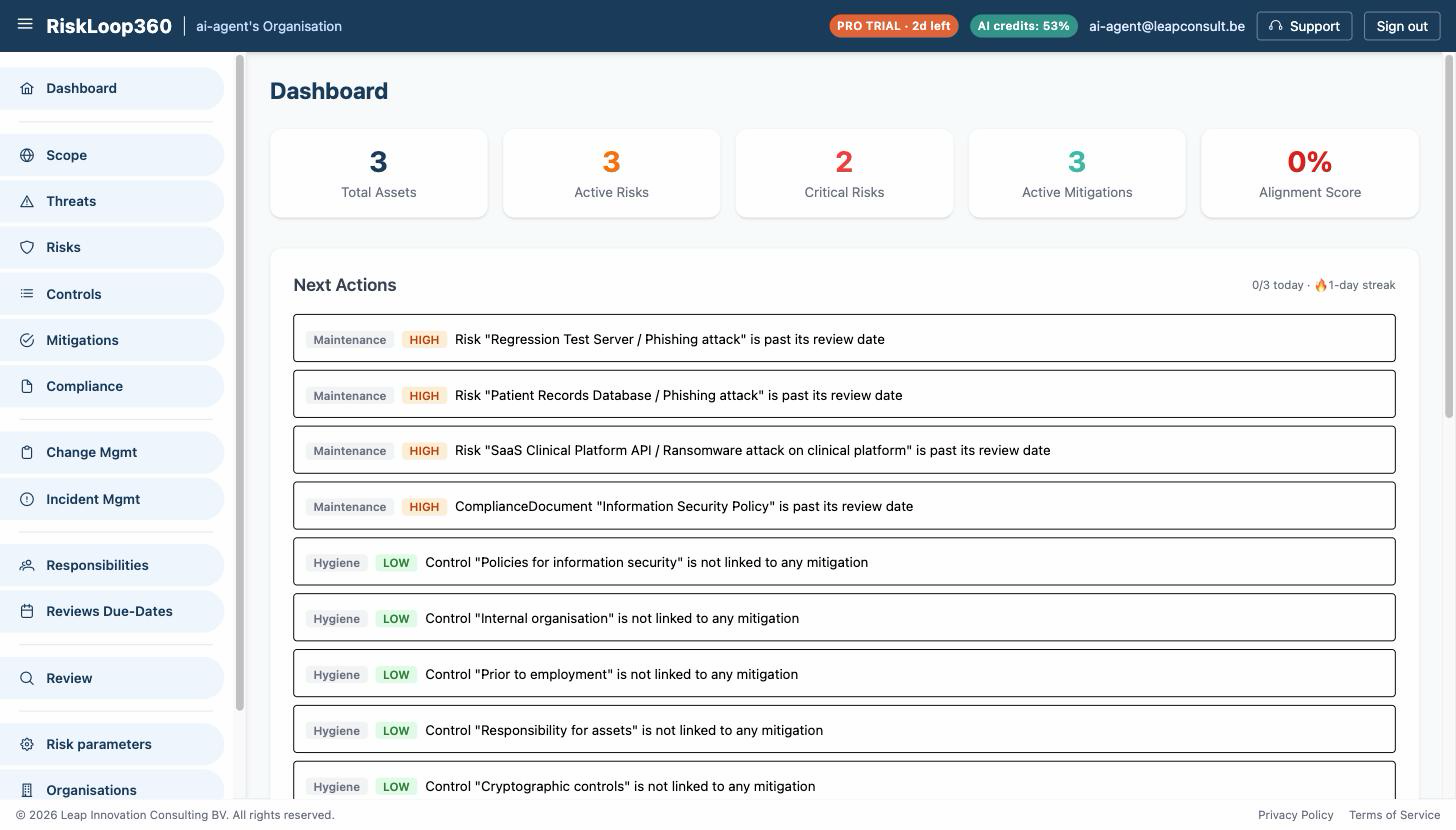
Real product screenshot — sample data shown
Built for teams working with
From scope to score, in your own words
A walk-through of a real onboarding, using a sample healthcare SaaS company as the example organisation.
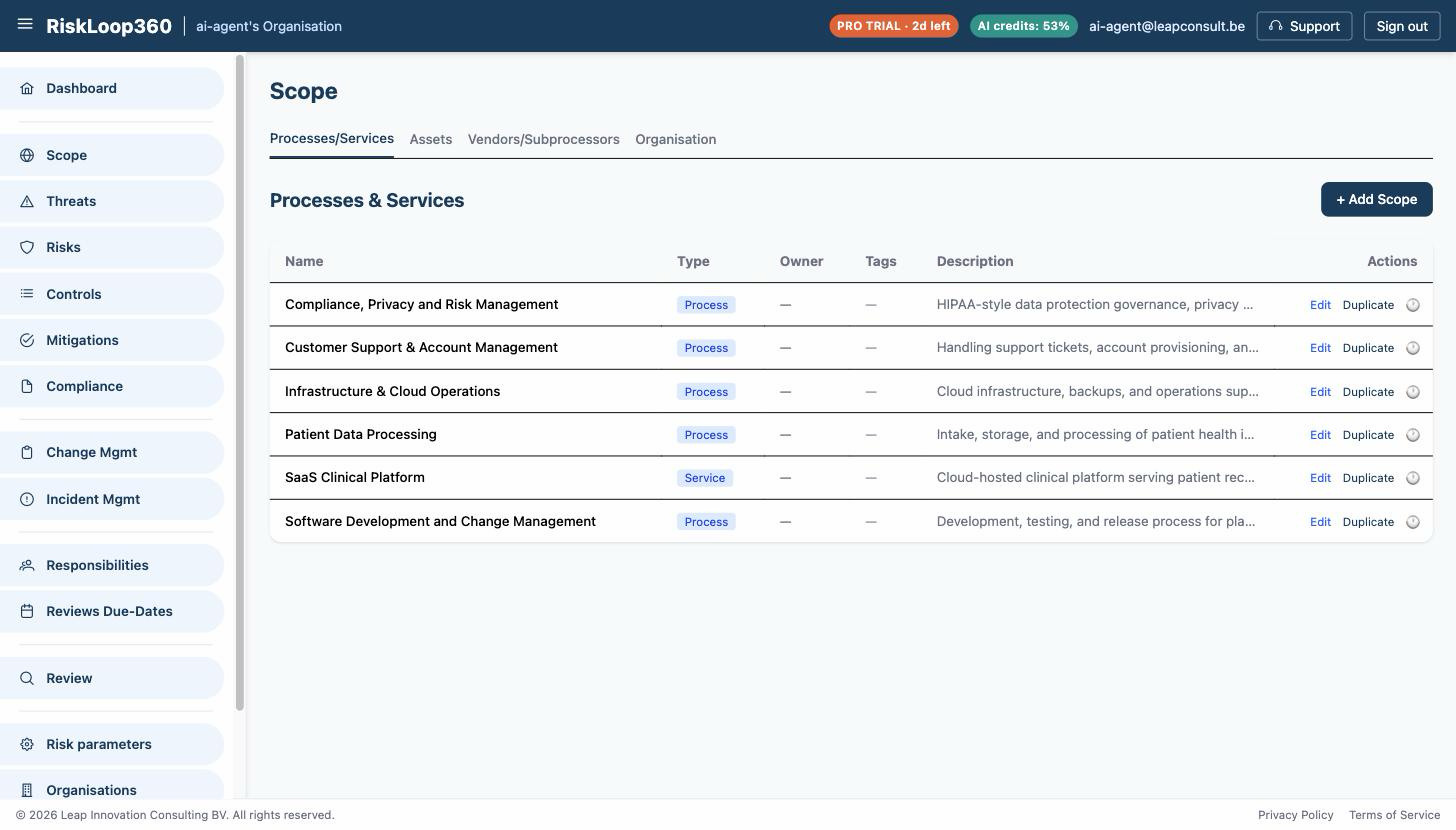
Describe your organisation, get a scope back
The guided onboarding wizard turns a plain-language description of your business into structured processes, services, and vendors — ready to review and edit, not a blank form to fill in from scratch.
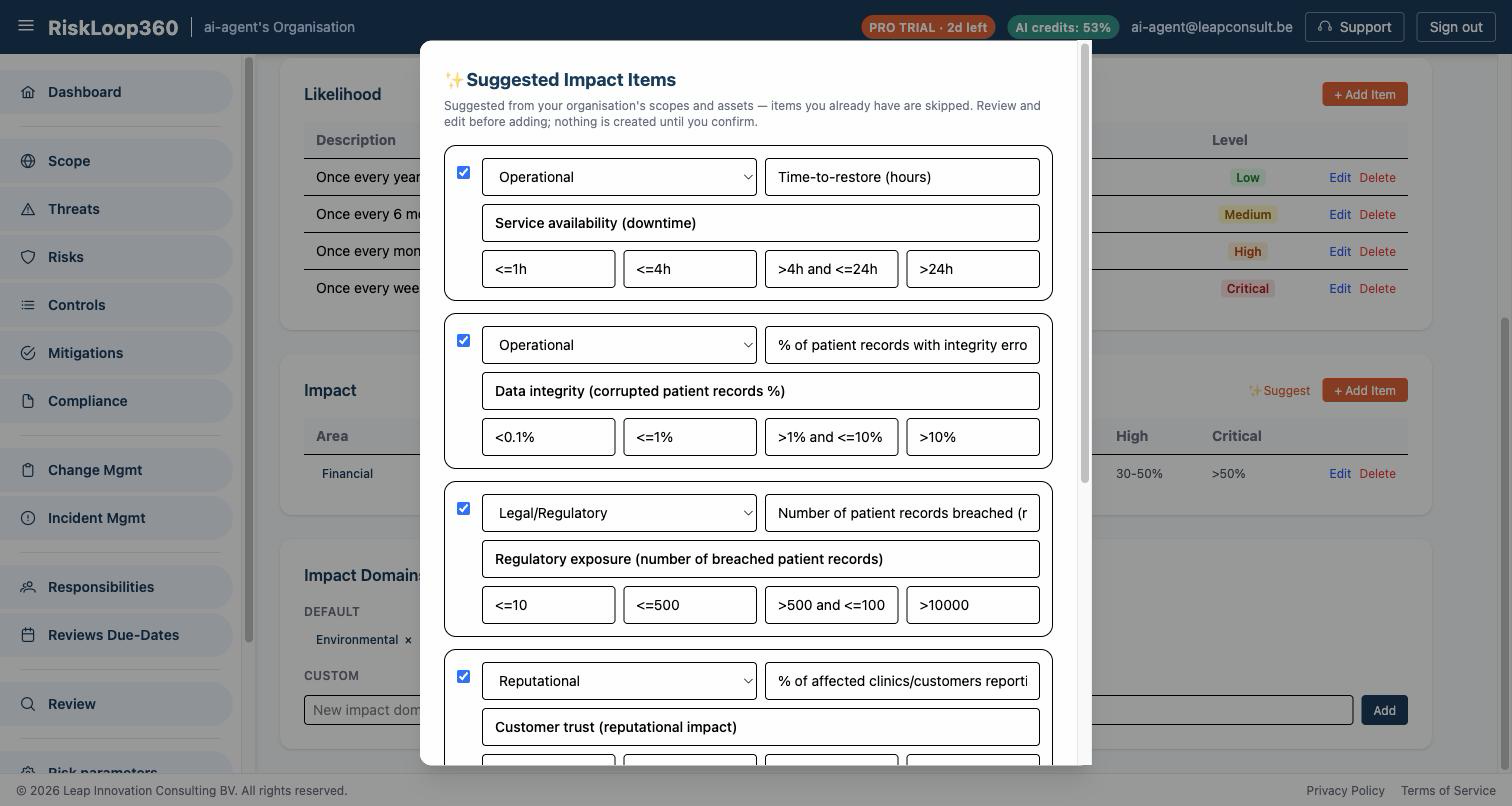
AI drafts your impact criteria — you stay in control
Based on the scopes and assets you've already entered, the AI Suggestion Layer proposes concrete, measurable impact thresholds (PHI exposure, downtime, churn, fines) across every impact domain. Nothing is created until you review and confirm.
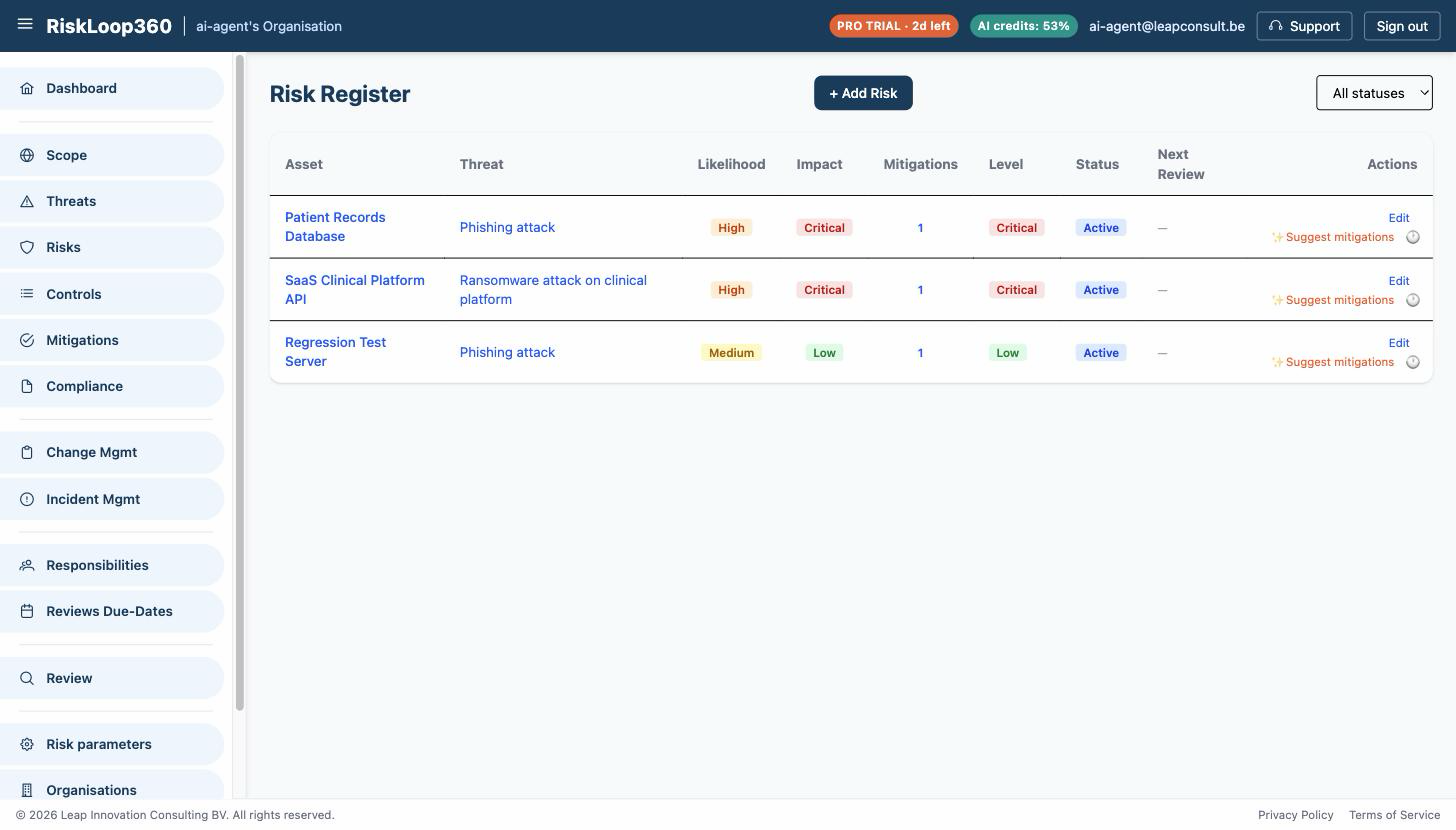
Every risk, scored the same way, every time
Pick an asset and a threat, check off the checklist items that apply, and RiskLoop360 computes the score and level from your organisation's risk matrix — no spreadsheets, no inconsistent judgement calls between reviewers.
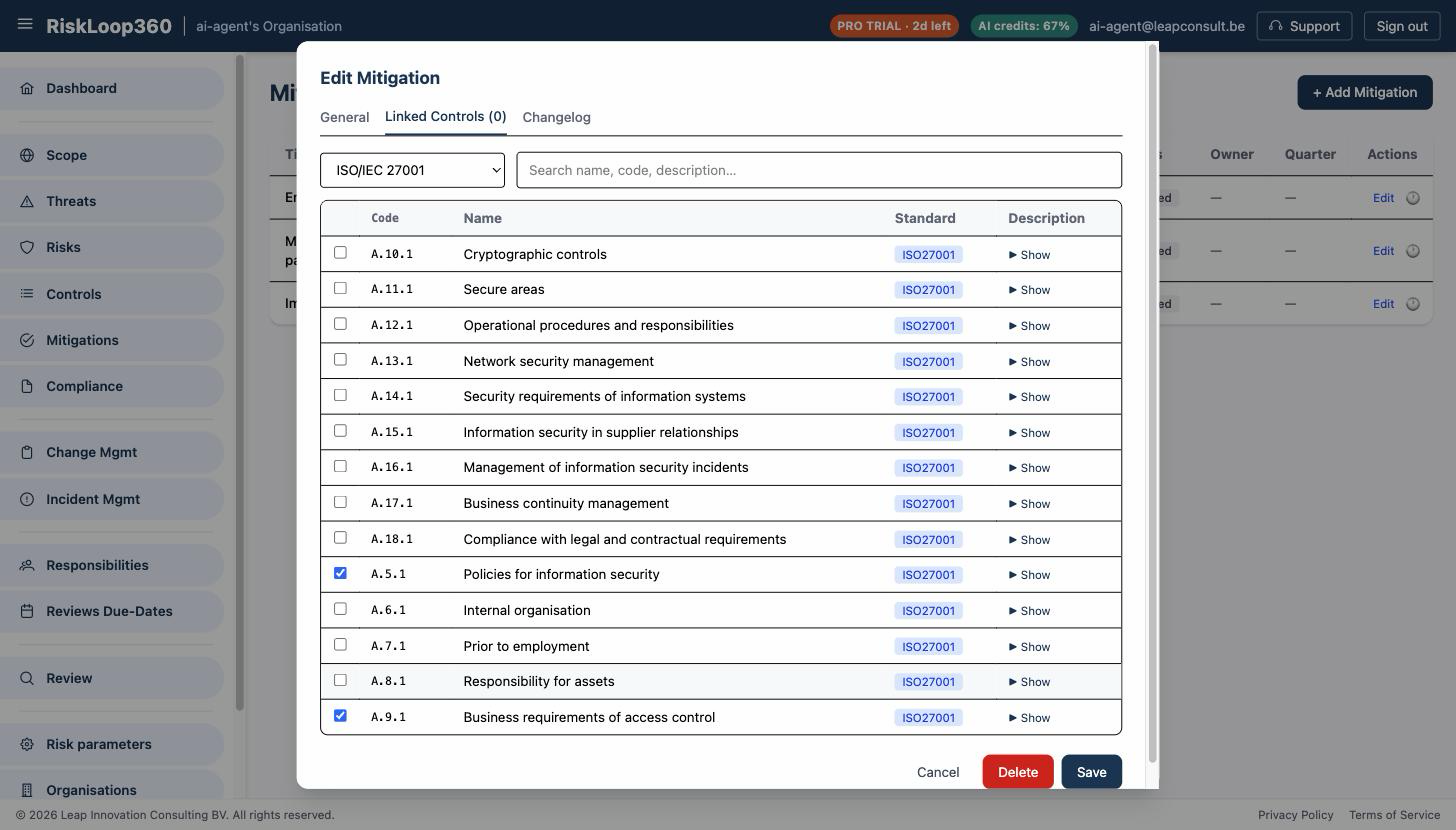
Link mitigations straight to the controls that need them
Every mitigation can be mapped to paraphrased controls across ISO 27001, ISO 27701, and more — filterable by standard, searchable by code or name — so your compliance posture updates itself as you close risk.
Everything your risk management system needs — nothing it doesn't
From guided onboarding to internal audit and management review, RiskLoop360 covers the full lifecycle of information security and privacy risk management.
Guided Onboarding Wizard
Describe your organisation and the wizard drafts your scope, assets, impact domains, and risk checklist for you — go from signup to a working risk management system in minutes, not weeks.
Scope, Asset & Vendor Register
Define the processes, services, assets, and vendors/subprocessors in scope for your risk management system. Tag everything by customer, project, or domain for precise filtering.
Threat & Risk Assessment Engine
Pair assets with threats, check off the likelihood and impact criteria that apply, and let a configurable risk matrix score and prioritise every risk consistently.
AI Suggestion Layer
Every register can be AI-assisted: suggested assets from a scope, threats & risks from an asset, mitigations from a risk, impact criteria from your context. You always review and confirm before anything is created.
Mitigation Tracking
Assign, track, and close mitigations over time, with a residual (post-mitigation) risk estimate so you can see the impact of remediation before it's even finished.
Control Framework Mapping
Link every mitigation to paraphrased controls across 12+ standards — ISO 27001, 27701, 42001, 27017/18, NIST CSF, SOC 2, GDPR, NIS 2, and more. See compliance posture across every framework at once.
Policy & Procedure Generator
Auto-generate policies and procedures from your risk register and mitigations. Link headings directly to specific controls for full traceability.
Audit-Ready PDF Export & Version Control
Export polished PDF policies with automatic version numbering. Every change to the risk register and policy documents is timestamped, attributed, and comparable.
Change & Incident Risk Checklists
Embed contextual risk checklists directly into your change and incident management workflows, so risk is assessed at the moment it's introduced — not after the fact.
Internal Audit & Management Review
Plan and record internal audits with findings (Clause 9.2), and run periodic management reviews with tracked decisions (Clause 9.3) — the evidence trail auditors ask for.
Corrective Action (CAPA) Tracking
Turn audit findings, review actions, and incidents into tracked nonconformities with required effectiveness verification before a corrective action can close (Clause 10.2).
Roles, Responsibilities & Review Due-Dates
Assign primary and backup owners to assets, threats, risks, and documents, with review due-dates that surface overdue records before an auditor finds them first.
Actionable Dashboard
Summary stats, alignment score, and a prioritised Next Actions list — overdue reviews, unmitigated risks, compliance gaps — turn "how are we doing" into "what do I do next".
Multi-Tenant, Role-Based Workspace
Invite your team with Admin, Contributor, or Employee roles per organisation, so access matches responsibility instead of everyone sharing one login.
AI Clarifying Questions & 5-Whys Root-Cause
The Change wizard asks follow-up questions when your description is too thin before running an impact analysis, and incidents get an AI-drafted 5-whys root-cause chain with a coverage verdict — conclusions grounded in specifics, not guesses.
Meet any auditor's expectations
RiskLoop360 ships with paraphrased control libraries for the most widely adopted security, privacy, and quality frameworks, with more added regularly.
ISO/IEC 27001
Information security management requirements and Annex A controls for your risk management system.
ISO/IEC 27701
Privacy information management extension to ISO 27001 for GDPR and global privacy compliance.
ISO/IEC 42001
AI management system requirements — manage risks from artificial intelligence systems.
ISO/IEC 27017 & 27018
Cloud security controls and protection of PII in public cloud, for cloud service providers and tenants.
ISO 22301, 13485 & 9001
Business continuity, medical device quality, and general quality management controls.
NIST Cybersecurity Framework
Identify, Protect, Detect, Respond, Recover — full CSF function and category coverage.
SOC 2
Trust services criteria mapped to your mitigations, ready for your next Type I or Type II audit.
GDPR & NIS 2
EU data protection and network-and-information-security obligations, mapped alongside your other frameworks.
More coming
CIS Controls, DORA, and additional frameworks on the roadmap. Request yours →
The loop, not a one-time project
Most risk registers go stale the week after the audit. RiskLoop360 is built so step 5 feeds back into step 1 — risk management stays current instead of expiring.
Scope & identify
Onboard your organisation, then populate assets, threats, and vendors — AI-assisted or manual.
Score & prioritise
Rate likelihood and impact against your own checklist. Let the matrix rank risks so you focus on the right ones.
Mitigate & map controls
Assign mitigations, link them to framework controls, and track residual risk as work progresses.
Document & export
Generate versioned policies from your risk register and export audit-ready PDFs on demand.
Audit, review & loop back
Run internal audits and management reviews, track corrective actions, and let due-dates pull you back to step 1.
Simple, seat-based pricing
Every paid plan includes 5 seats. Need more people in the loop? Additional seats are $50/month.
Free
Land-and-expand — competes directly with Eramba Community and spreadsheets.
- ✓ Risk register, assets, threats, controls, compliance docs
- ✓ Change/Incident evaluations
- ✓ Mitigations — capped at 20
- ✓ AI onboarding wizard suggestions
Base
Everything you need to run a live risk register, unlimited.
$790/yr paid annually — 2 months free
- ✓ Everything in Free
- ✓ Unlimited mitigations
- ✓ 5 seats included
- ✗ In-app AI suggestions, Internal Audit, Management Review, CAPA
Pro
Full AI suggestions plus audit, review, and CAPA workflows.
$3,490/yr paid annually — 2 months free
- ✓ Everything in Base
- ✓ In-app AI suggestions (assets, threats, mitigations, change-impact)
- ✓ Internal Audit, Management Review, CAPA
- ✓ 5 seats included
Enterprise
Private hosting and SSO for organisations with stricter requirements.
- ✓ Everything in Pro
- ✓ Private hosting
- ✓ SSO
- ✓ Negotiated seats & pricing
All paid plans include 5 seats. Additional seats are $50/month each. Enterprise seat count and pricing negotiated per contract.
| Feature | Free | Base | Pro | Enterprise |
|---|---|---|---|---|
| Risk register, assets, threats, controls, compliance docs | ✅ | ✅ | ✅ | ✅ |
| Change/Incident evaluations | ✅ | ✅ | ✅ | ✅ |
| Mitigations | Capped at 20 | Unlimited | Unlimited | Unlimited |
| AI — onboarding wizard suggestions | ✅ | ✅ | ✅ | ✅ |
| AI — in-app suggestions (assets, threats, mitigations, change-impact) | ✗ | ✗ | ✅ | ✅ |
| Internal Audit | ✗ | ✗ | ✅ | ✅ |
| Management Review | ✗ | ✗ | ✅ | ✅ |
| CAPA (Corrective Actions) | ✗ | ✗ | ✅ | ✅ |
| Private hosting & SSO | ✗ | ✗ | ✗ | ✅ |
| Seats included | — | 5 | 5 | Negotiated |
| Additional seat | — | $50/month | $50/month | Negotiated |
Ready to take control of your risks?
Join the early-access programme and be first to experience RiskLoop360. Leave your details and we'll be in touch.
Accept cookies to load the contact form.